Droid 推出自动化安全审查功能
Introducing Automated Security Review
Droid 在每个非草稿 PR 中运行基于 STRIDE 的安全审查,发现漏洞会附带严重程度、CWE 参考编号、解释和修复建议,并作为内联评论直接发布在代码差异上。该功能已在生产代码库中运行,发现 CVE-2026-42876 等漏洞。Droid 通过构建轻量级威胁模型、扫描漏洞并验证候选发现来过滤误报,每个 PR 只生成一个汇总评论。
By Nizar Alrifai, Shashank Sharma - June 11, 2026 - 2 minute read
Product
Share
The most dangerous security bugs often look like ordinary code review details: a missing authorization check, a user-controlled string crossing a trust boundary, or a token logged where it should never appear.
Today we're rolling out automated security review in Droid. On every non-draft PR, Droid runs a STRIDE-based security review alongside the standard code review. Findings come back with severity, a CWE reference, an explanation, and a suggested fix, posted as inline comments directly on the diff.
Real-world audits
Droid security review has been run across production codebases, surfacing findings that went through responsible disclosure. A few that went public:
- CVE-2026-42876 — external-secrets: An attacker with nothing more than ExternalSecret create permissions could weaponize a template injection path, forcing the Kubernetes operator to mint persistent service account tokens and impersonate any service account in the entire namespace.
- workos/workos-node#1578 — WorkOS Node SDK re-serialized request bodies before HMAC verification, silently breaking webhook signature checks and rejecting legitimate deliveries.
"Thank you for your submission and the detailed technical analysis you provided. Your report demonstrates strong security research skills with clear reproduction steps, proof-of-concept code, and thorough impact assessment." — maintainers of projects Droid has audited
These are a fraction of total findings. In addition to what goes public, Droid surfaces private findings disclosed through responsible channels that remain embargoed until owning projects are ready.
How it works
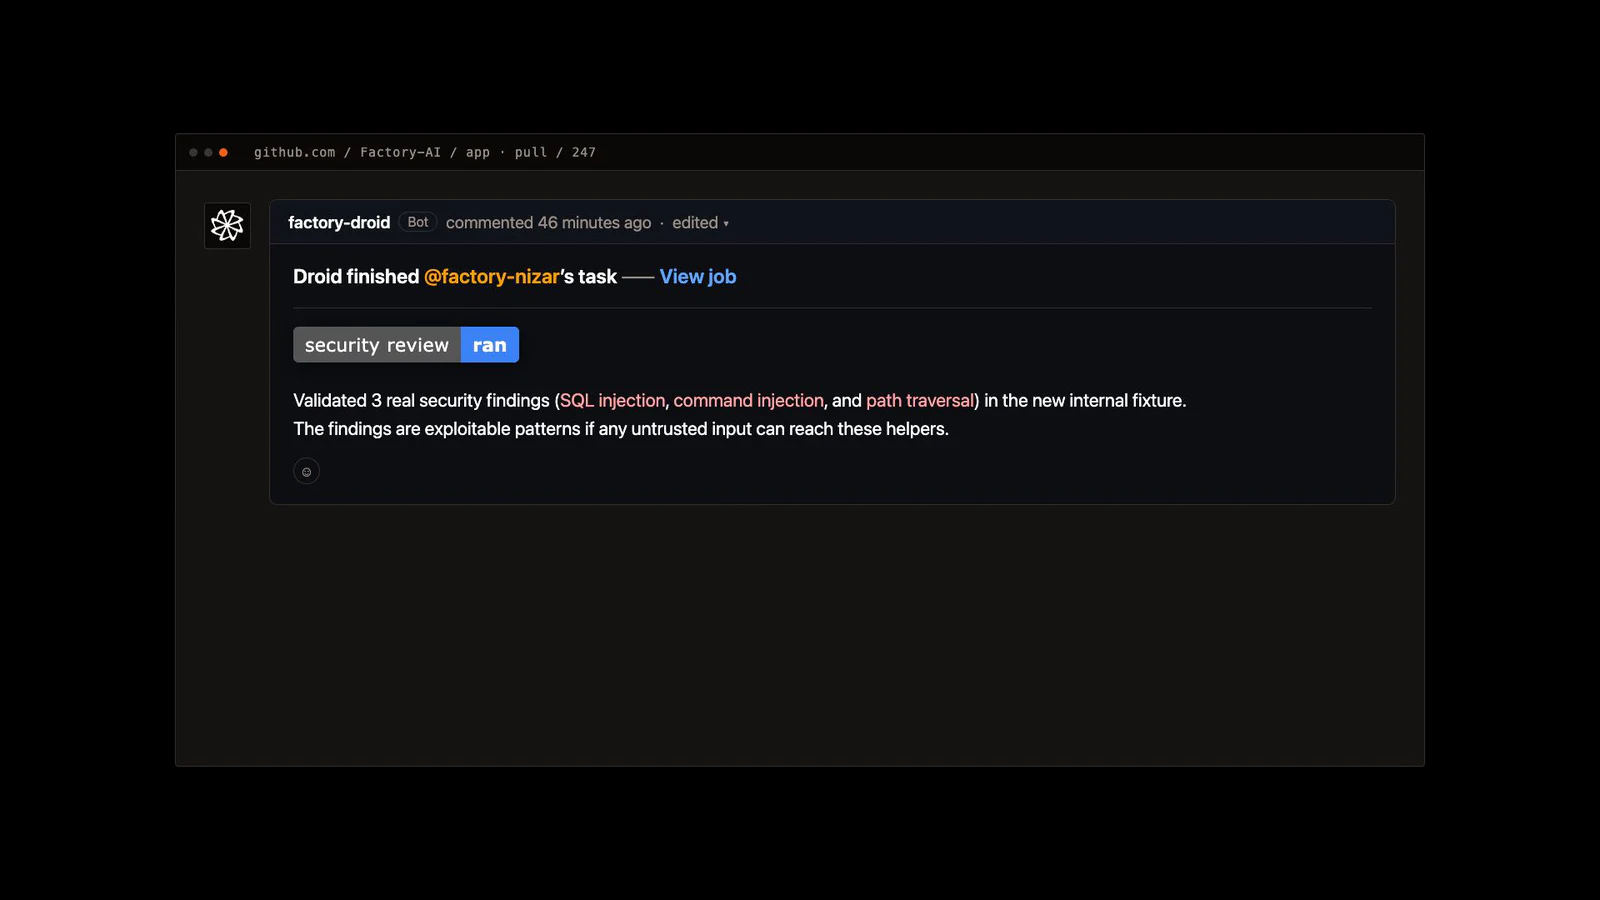
Droid builds a lightweight threat model of the changed surface, scans for vulnerabilities (OWASP Top 10, OWASP LLM Top 10, injection, broken auth, secrets in logs), then validates each candidate finding against the diff to filter false positives before posting. One deduplicated summary per PR.
When something is caught
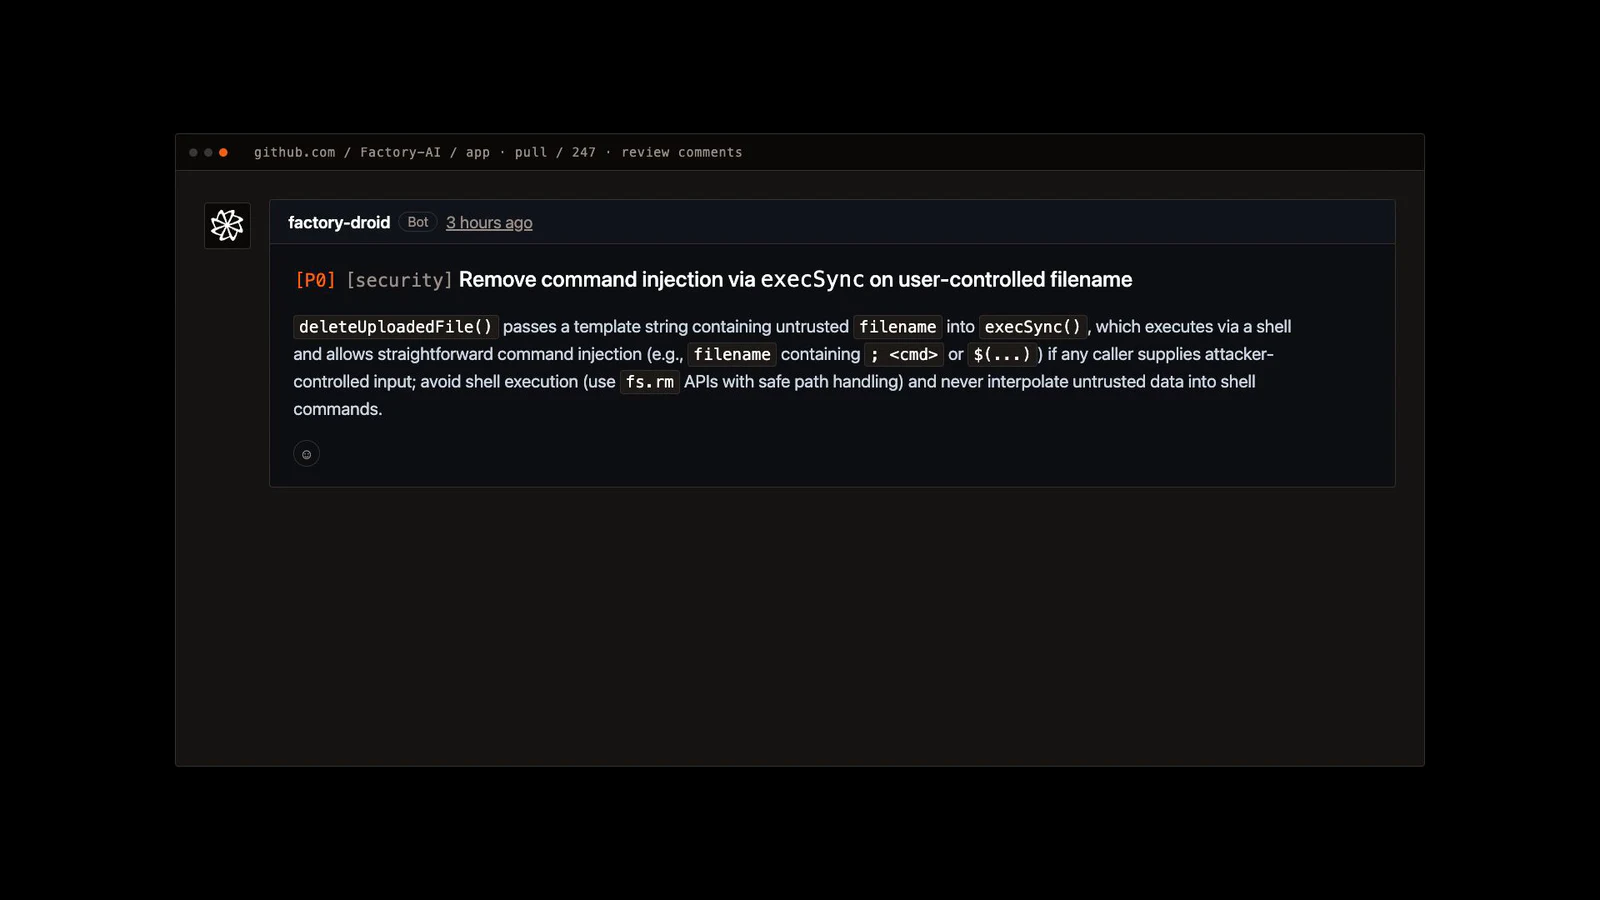
Droid posts an inline review comment with a priority tag, the area, and a plain-language explanation referencing the actual symbols and call sites involved:
Setup
In the Droid CLI / Desktop App
One-time setup. Detects your repo platform, installs the GitHub App (or configures GitLab), generates workflows, and opens a PR to merge.On-demand audit. Run in any local session. Reviews the entire repo or just the current diff.
Regular codebase audits on GitHub
For scheduled full-repository audits in GitHub Actions, see the Security Review docs.
For the best coverage, Droid runs a deep security audit across an entire repository. This uses orchestrated multi-agent missions that scan every source file, cross-reference findings, and validate exploitability before reporting.
Run it with /security-review deep audit inside a Mission.
Automated security review is available today on all plans. Security review is the first line of defense, but building software autonomously means applying the same rigor at every step. That's what Factory is building — a complete development system where every stage is automated, verified, and continuously improving.
Read the full docs to learn more.
来源: Factory News · factory.com