Interconnects6565
Are the security concerns triggered by the Claude Mythos open-source model exaggerated?
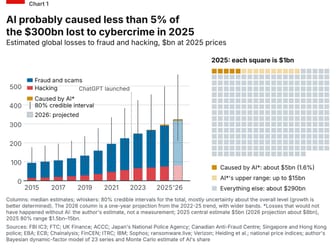
After the open-source Claude Mythos model was released, claims that it could pose significant cybersecurity risks were widely spread, but the author believes these concerns are exaggerated. GLM-5.3 is the model that truly crosses the capability threshold, and if the open-source Mythos is leaked, it will bring more acceleration of existing risks rather than a qualitative change. The author points out that although there have been frequent cybersecurity incidents recently, the AI security community's reaction to open-source models has not reached a 'disaster' level, and actually exploiting model vulnerabilities to attack requires a combination of multiple factors, and the current situation is more like 'headache' than 'real disaster'.